
Article
Apply the right level of scrutiny to every interaction across every channel to protect your customers from fraud and reduce friction.
When authentication only happens at login, it creates vulnerabilities that sophisticated fraudsters can exploit. At the same time, one-size-fits-all controls treat even legitimate customers as suspicious actors, causing unnecessary friction.
Alloy’s adaptive, risk-based authentication unifies identity and fraud signals into a single decisioning layer, so every customer action is evaluated in full context and is met with the right level of scrutiny and friction for the risk presented in that moment.

Alloy enriches and unifies signals like device intelligence, behavioral biometrics, network and geolocation, account activity into a single view to help make more informed decisions about the riskiness of a user at any given point.
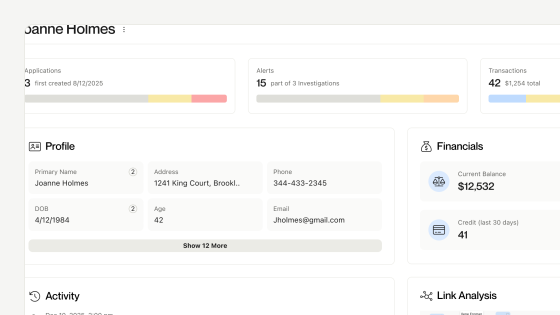
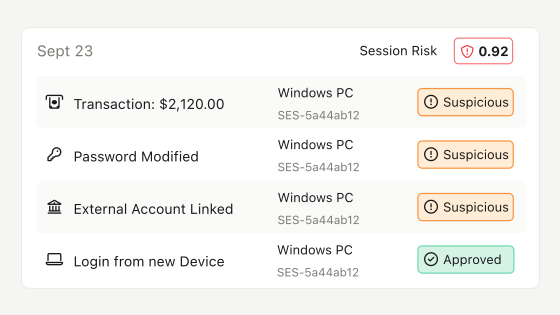
Evaluate trust beyond login at the moments that matter most, like password resets, contact detail changes, external account linking, and high-value transactions. Alloy’s cross-channel visibility ensures your risk policy is enforced consistently across human and non-human channels.
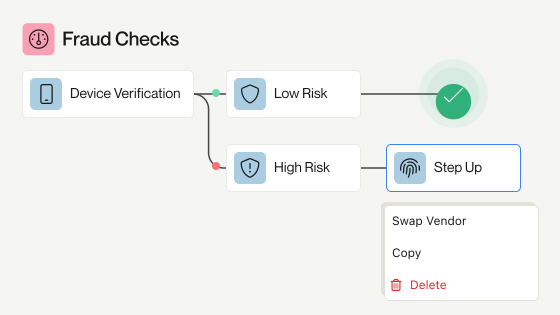
Alloy dynamically enforces the right level of friction so low-risk users sail through authentication while higher-risk activity triggers step-up. Enforcement happens in real time through the Alloy SDK, and you can easily switch between vendors to improve STP or meet evolving business needs.
Alloy enriches and unifies signals like device intelligence, behavioral biometrics, network and geolocation, account activity into a single view to help make more informed decisions about the riskiness of a user at any given point.
Evaluate trust beyond login at the moments that matter most, like password resets, contact detail changes, external account linking, and high-value transactions. Alloy’s cross-channel visibility ensures your risk policy is enforced consistently across human and non-human channels.
Alloy dynamically enforces the right level of friction so low-risk users sail through authentication while higher-risk activity triggers step-up. Enforcement happens in real time through the Alloy SDK, and you can easily switch between vendors to improve STP or meet evolving business needs.
Our machine learning model, Fraud Signal, continuously scores customers on their evolving fraud risk, so your team spends less time on manual review and more time on the cases that actually warrant scrutiny. The Fraud Signal score extends from the time a customer onboards across login, account changes, and money movement, so every authentication decision reflects the customer's full history.
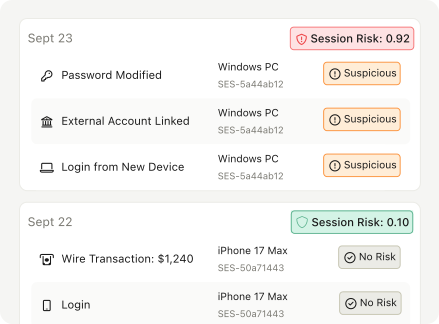
Alloy adds risk context to new-device logins and account-recovery attempts using device, behavioral, and historical signals. Customers whose activity is consistent with their profile can resolve access issues through self-service, while higher-risk attempts can be stepped up for additional verification.
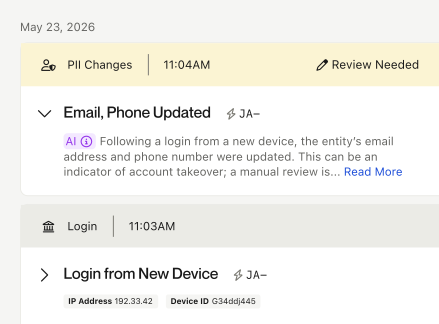
A fraudster with account access rarely announces themselves, they just change a phone number or email through a low-friction channel. Alloy applies the same verification scrutiny to that change as it would to a new account and logs every step for audit.

Linking an external account is one of the highest-risk moments after onboarding, since it's a direct path to money movement. Alloy can run ownership, access, and risk checks before any linkage completes, blocking or pausing risky connections the moment something looks off.

Adding a signer shouldn't get lighter scrutiny just because the account already exists. Alloy runs the same CIP, KYC, and fraud checks used at onboarding, all in real time, across every channel a signer could be added from.
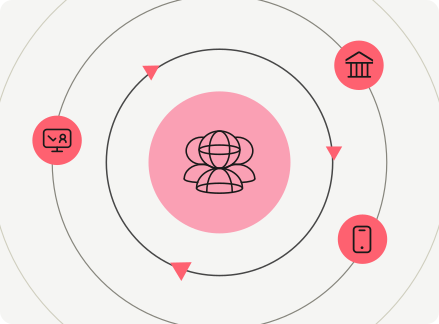
An address change in the contact center, a login from a new device, and an online account request are not treated like separate events. Alloy evaluates them as one connected sequence across digital, call center, and branch interactions, using consistent policies and shared risk context to identify escalating account takeover attempts while enabling seamless, self-serve experiences for low-risk customers.
Alloy adds risk context to new-device logins and account-recovery attempts using device, behavioral, and historical signals. Customers whose activity is consistent with their profile can resolve access issues through self-service, while higher-risk attempts can be stepped up for additional verification.
A fraudster with account access rarely announces themselves, they just change a phone number or email through a low-friction channel. Alloy applies the same verification scrutiny to that change as it would to a new account and logs every step for audit.
Linking an external account is one of the highest-risk moments after onboarding, since it's a direct path to money movement. Alloy can run ownership, access, and risk checks before any linkage completes, blocking or pausing risky connections the moment something looks off.
Adding a signer shouldn't get lighter scrutiny just because the account already exists. Alloy runs the same CIP, KYC, and fraud checks used at onboarding, all in real time, across every channel a signer could be added from.
An address change in the contact center, a login from a new device, and an online account request are not treated like separate events. Alloy evaluates them as one connected sequence across digital, call center, and branch interactions, using consistent policies and shared risk context to identify escalating account takeover attempts while enabling seamless, self-serve experiences for low-risk customers.
“Alloy gives us visibility and control we simply didn't have before. Instead of fragmented signals and siloed decisions, we get a unified view of an entity’s risk profile that unlocks faster decision-making, better collaboration across teams, and the ability to test and optimize without disrupting the member's experience.”
Eva Coffee Manager of Digital Strategy, Suncoast Credit Union
17%
Increase in new digital membership completion rates
35%
Decrease in fraud losses
91%
Increase in new member digital loans
Whether it’s an unrecognized IP address, a new device, or an unusual location, sometimes a login attempt just doesn't add up. Alloy dynamically orchestrates the right adaptive authentication response to each access attempt from a range of pre-built integrations.
Ready to make authentication faster for customers, harder for fraudsters, and easier on your teams?
Article


Risk-based authentication (sometimes abbreviated as RBA) is an approach that dynamically adjusts the level of scrutiny applied to each interaction based on the risk it presents. Rather than applying the same controls to every login or transaction, risk-based authentication evaluates signals — device, behavior, location, and history — to determine how much friction is appropriate. Low-risk interactions move through seamlessly, while higher-risk ones trigger additional verification.
Your CIAM is built to manage credentials and confirm that the person logging in matches what's on file. Alloy assesses whether that interaction should be trusted in the first place. By layering identity, device, and behavioral signals from onboarding and throughout the lifecycle onto your CIAM's credential check, Alloy provides the risk context your CIAM wasn't built to evaluate and triggers step-up when something doesn't add up.
Agentic AI is making risk-based authentication more complex, since any account interaction may be initiated by an agent acting on a customer's behalf. As agents take on more customer-facing actions, institutions still need to evaluate valid credentials, but also need to assess the signals, behavior, and requested action of an agent to determine the appropriate level of authorization and access to a customer's account.
Yes. Alloy isn’t a credential manager or an access control system — it’s an identity risk layer. It evaluates the identity signals your existing tools don’t, then feeds that context back into the workflow, so your CIAM, IdP (Identity Provider), IVR (Interactive Voice Response), and other downstream systems can make smarter decisions. You keep what you have, and Alloy makes it work better.
MFA is a specific verification method that confirms identity using two or more factors, like a password and a one-time code. Risk-based authentication is a broader strategy that dynamically determines when and how much verification is needed based on the signals present. MFA is one tool within a risk-based authentication program that triggers selectively when risk signals warrant it.
By evaluating context rather than applying blanket controls, risk-based authentication can recognize low-risk interactions (like a known device, a familiar location, consistent behavior) and let those customers through without additional steps. Friction is reserved for the interactions that genuinely warrant it, which means trusted customers spend less time jumping through aggravating hoops.
Alloy centralizes your risk logic in one place, so policy changes can be deployed in minutes rather than engineering sprints. By automating risk response and enabling customer self-resolution through intelligent step-up, Alloy also reduces the volume of cases that require manual review — freeing your team to focus on what actually needs human judgment.